
Zazy-Pentest-Plugin-for-Claude
A Claude Code plugin for authorized pentesting, bug bounty and red teaming - 318 attack skills across web, API, Android, iOS, network, AD, cloud and wireless…
Install with your AI
Paste into Claude Code, Cursor, or any agent — it reads the repo and wires the tool into your project.
Install and set up Zazy-Pentest-Plugin-for-Claude (claude-plugin project) into my current project.
Found on https://claudeers.com/zazy-pentest-plugin-for-claude
Repo: https://github.com/AnandJogawade/Zazy-Pentest-Plugin-for-Claude
Homepage/docs: https://github.com/AnandJogawade/Zazy-Pentest-Plugin-for-Claude
Detected install method: claude-plugin → /plugin install zazy-pentest-plugin-for-claude@AnandJogawade/Zazy-Pentest-Plugin-for-Claude
Category: plugins. Platforms: api, web, mobile.
Read the repo's README for exact setup and env vars, then install it and wire it into my project.

Claudeers Health Verdict:
unknown; community-verified: false. Confirm the source before running anything.
⚠ Unverified / not recently updated — review before pasting a run-this config.
/plugin marketplace add AnandJogawade/Zazy-Pentest-Plugin-for-Claude
/plugin install zazy-pentest-plugin-for-claude@AnandJogawade/Zazy-Pentest-Plugin-for-Claude
git clone https://github.com/AnandJogawade/Zazy-Pentest-Plugin-for-Claude
// compatibility
| Platforms | api, web, mobile |
|---|---|
| Operating systems | — |
| AI compatibility | claude |
| License | MIT |
| Pricing | open-source |
| Language | Python |

The most complete offensive-security plugin for Claude Code.
AI-powered penetration testing, bug bounty & red teaming — 318 attack skills, 19 dynamic payload libraries, CVE/component auditing, a true-positive verifier agent, and an autonomous recon-to-report workflow across web, API, Android, iOS, network, Active Directory, cloud & wireless.
Quickstart • Categories • How it works • FAQ • License • Legal
⚠️ Authorized use only. The plugin is for systems you own or have written permission to test. Every engagement starts with
/zazy-scopeto record authorization and rules of engagement. See the Legal Disclaimer.
✨ Why zazy-pentest is different
Most security "skills" ship a thin checklist and four or five static payloads — so the AI does one shallow pass and stops at the first positive. zazy-pentest tests like a real operator:
| A typical pentest skill | 🔥 zazy-pentest |
|---|---|
| A short checklist | A full Recon → Map → Probe → Exploit → Chain → Verify → Report loop per skill |
| 4–5 static payloads | 19 payload libraries + rules to generate context-aware variants, encodings & WAF bypasses |
| Stops at the first finding | Explicitly chains every finding toward maximum impact |
| "Likely vulnerable" | A verifier agent re-confirms via a second method or OAST before reporting |
| One surface | Web, API, mobile, network, AD, cloud & wireless in one plugin |
| Answers from memory | Runs your real tools (WSL/Kali, HexStrike MCP, Burp MCP) and reads their output |
⚡ Features
- 🧠 318 attack skills covering the modern offensive-security surface.
- 🧪 19 dynamic payload libraries — XSS, SQLi, NoSQL, SSRF, SSTI, XXE, deserialization, file-upload, command-exec, LDAP/XPath/XSLT, CRLF/HTTP, client-side, JWT/auth, GraphQL + a dedicated WAF-bypass and OOB/OAST set.
- 🛰️ Autonomous recon-to-report — one command runs the whole engagement.
- ✅ True-positive verifier agent — kills false positives before they reach the report.
- 🧩 CVE & component auditing — fingerprints tech & dependencies and maps them to CVEs.
- 🛠️ Flexible backends — native Kali, WSL+Kali, Kali-SSH, Kali/HexStrike/Metasploit MCP, Burp MCP, Windows fallback.
- 🎯 Tiered safety — full exploit, gated, or detection/safe-PoC.
🚀 Quickstart
Claude Code — plugin (recommended)
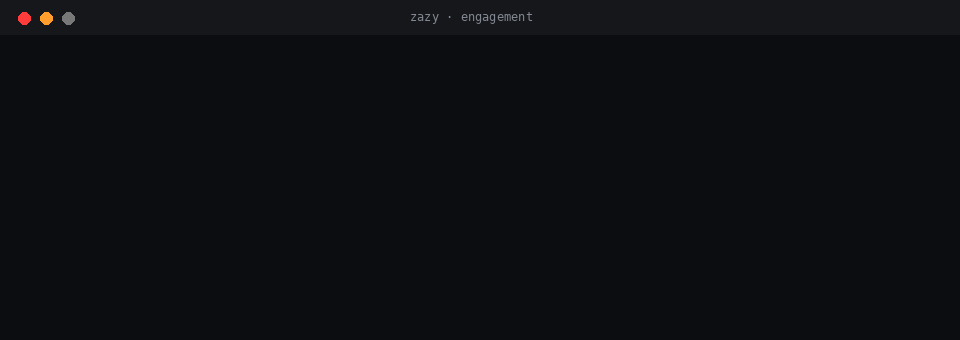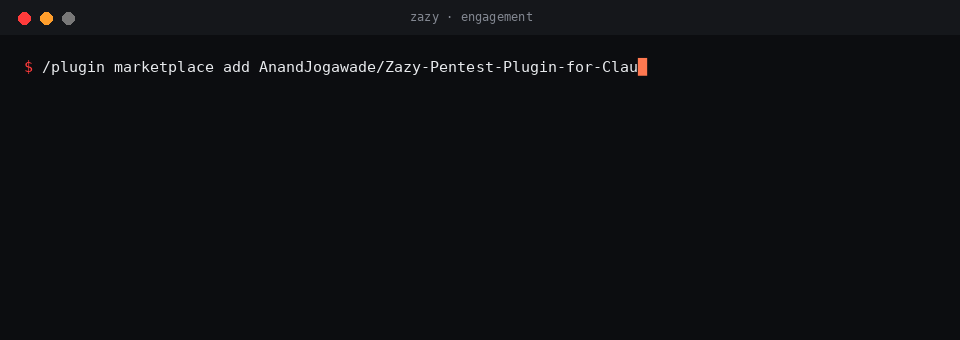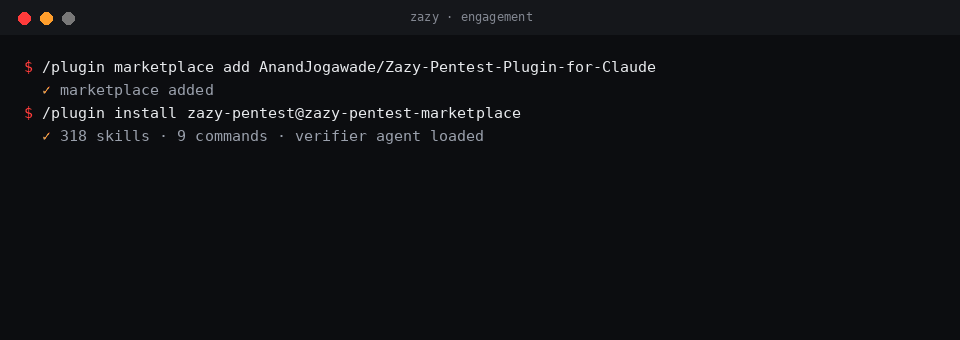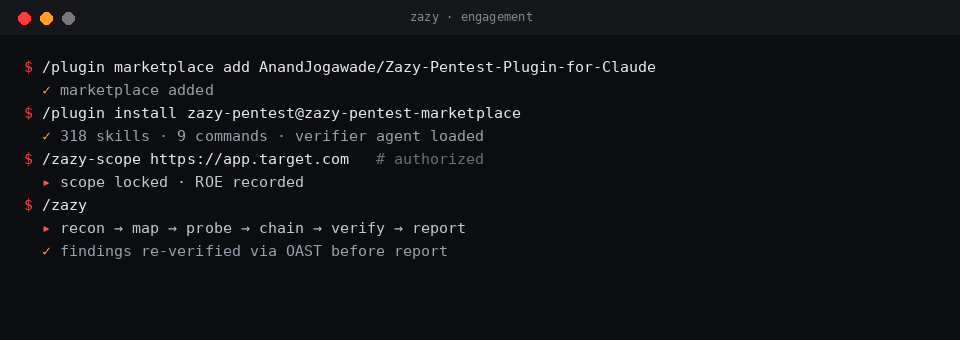
/plugin marketplace add AnandJogawade/Zazy-Pentest-Plugin-for-Claude
/plugin install zazy-pentest@zazy-pentest-marketplace
Reload Claude Code, then run an engagement:
/zazy-scope https://app.you-are-authorized-to-test.com
/zazy            # recon → test → chain → verify → report
Claude Code — from a local clone
git clone https://github.com/AnandJogawade/Zazy-Pentest-Plugin-for-Claude
/plugin marketplace add ./Zazy-Pentest-Plugin-for-Claude
/plugin install zazy-pentest@zazy-pentest-marketplace
Use a single skill manually (any Claude surface)
Pick any skill and paste it into your Claude Project / system prompt:
cat zazy-pentest/skills/file-upload/SKILL.md
Validate your copy (optional)
python3 zazy-pentest/scripts/validate_plugin.py     # self-test: manifests + skills
claude plugin validate ./zazy-pentest --strict       # authoritative check
🧰 What you can do with it
| Surface | What zazy-pentest tests |
|---|---|
| Web & client-side | XSS (reflected/stored/DOM/blind), SQLi & NoSQL, SSRF, SSTI, XXE, deserialization, file upload → RCE, path traversal/LFI, CSRF, prototype pollution, HTTP request smuggling, cache poisoning, auth/session/access-control, business logic |
| API | REST, GraphQL, SOAP/WSDL, WebSocket, gRPC — authz/IDOR, mass assignment, injection, schema abuse, rate-limit & JWT flaws |
| Mobile | Android & iOS static + dynamic analysis, WebView attacks, content-provider & IPC abuse, insecure storage, backend-API testing |
| Network & Active Directory | Service enumeration & exploitation, AD attack paths, Windows & Linux privilege escalation |
| Cloud & wireless | Cloud mis-config & credential exposure, Wi-Fi/wireless & IoT assessment |
| Components | Outdated/vulnerable servers, frameworks, libraries & third-party software → CVE mapping |
📚 Categories
| Category | Skills | Focus |
|---|---|---|
| Orchestration & core | 3 | Routing, scope, global verification & tiering |
| Reconnaissance & disclosure | 29 | OSINT, attack-surface mapping, exposed files & secrets |
| Web application | 112 | OWASP Top 10, client-side, business logic, advanced web classes |
| API | 22 | REST / GraphQL / SOAP / WebSocket / gRPC, authz, schema abuse, JWT |
| Android | 24 | Static & dynamic analysis, WebView, IPC, storage, backend |
| iOS | 23 | Static & dynamic analysis, keychain, IPC, transport security |
| Network & infrastructure | 34 | Service enumeration, exploitation & protocols |
| Active Directory | 17 | On-prem AD attack paths & abuse |
| Privilege escalation (Win/Linux) | 12 | Local privilege escalation on Windows & Linux |
| Cloud & containers | 5 | AWS / Azure / GCP mis-config, container & Kubernetes |
| Wireless & IoT | 15 | Wi-Fi/WPA, BLE, Zigbee, sub-GHz, embedded |
| Exploit development (Tier 2) | 8 | Memory corruption, ROP, mitigations, crash analysis |
| Red team (Tier 3) | 13 | Detection / safe-PoC / defense-validation |
| AI / LLM security | 1 | Prompt injection & model attacks |
| Total | 318 |
Full map in MINDMAP.md • complete list in INDEX.md.
🔄 How it works in a pentest
- 🎯 Scope —
/zazy-scoperecords authorized targets, rules of engagement & allowed tooling. Nothing runs outside it. - 🛰️ Recon — attack-surface mapping and deep web recon (crawl + analyze exposed files & logic).
- 🧪 Test — matching skills run with tiered depth, using the plugin's payload libraries first.
- 🔗 Chain — findings pushed toward maximum impact (e.g. upload → webshell → host → cloud).
- ✅ Verify — the verifier agent independently re-confirms each finding (second method / OAST) to remove false positives.
- 📄 Report — compiled into a client-ready report with evidence and remediation.
Tiering model
- Tier 1 — full authorized exploitation with safe PoC to confirm.
- Tier 2 — gated: the skill asks "lab / authorized to exploit?" → full exploitation if yes, else a dry scan.
- Tier 3 — detection / safe-PoC / defense-validation (
redteam-*), for authorized red-team and research contexts.
⌨️ Commands
| Command | What it does |
|---|---|
/zazy-scope | Define target, rules of engagement & tooling (run first, every time) |
/zazy | Full autonomous engagement |
/zazy-recon | Reconnaissance & attack-surface mapping |
/zazy-web | Focused web-application assessment |
/zazy-api | REST / GraphQL / SOAP / WebSocket / gRPC assessment |
/zazy-mobile | Android and/or iOS assessment |
/zazy-network | Network, service & infrastructure assessment |
/zazy-components | Outdated / vulnerable component & CVE audit |
/zazy-report | Compile findings into a client-ready report |
🧩 Recommended environment
| Component | Purpose |
|---|---|
| Claude Code | Runs the plugin |
| Execution backend | WSL + Kali, Kali via SSH, Claude Code installed directly in Kali, or a Kali / HexStrike / Metasploit MCP |
| HexStrike MCP | Bridges ~150 security tools to Claude as callable tools |
| Burp Suite MCP (optional) | Proxy history + manual Repeater PoCs |
| SecLists | Wordlists used across recon/content-discovery |
| High reasoning effort | Agentic chaining needs the model to think between tool calls |
❓ FAQ
Is zazy-pentest legal to use? Yes — for systems you own or are authorized in writing to test. Unauthorized testing is illegal everywhere. See the disclaimer.
Do I need Kali? You need an execution backend for real tools — WSL+Kali or the HexStrike MCP are recommended. The plugin orchestrates; your toolchain executes.
Does it work for bug bounty? Yes. Scope it to the program's in-scope assets with /zazy-scope and run /zazy or the focused commands.
How is this better than running tools manually? It chains findings, generates context-aware payloads, and verifies true positives automatically — turning a one-pass scan into an operator-style assessment.
Will it exploit things without asking? Tier-2 skills gate on authorization; Tier-3 are detection/safe-PoC. You stay in control via /zazy-scope.
📂 Repository layout
zazy-pentest/
├── .claude-plugin/plugin.json   # plugin manifest
├── skills/<name>/SKILL.md        # 318 methodology skills (flat)
├── commands/                     # 9 slash commands
├── payloads/                     # 19 reusable payload libraries
├── agents/verifier.md            # true-positive verifier subagent
└── scripts/validate_plugin.py    # self-test
.claude-plugin/marketplace.json   # marketplace manifest
📝 License
MIT — use freely, attribution appreciated. See LICENSE. Offensive content is provided for authorized testing only; see the Security Policy and Legal Disclaimer.
🛡️ Security
Found a problem in this repo (a bad payload, a leaked credential, an unsafe default)? Please report it privately — see SECURITY.md.
📜 Changelog
See CHANGELOG.md.
⚠️ Legal Disclaimer
This project is provided strictly for authorized security testing, education, and research.
By downloading, installing, or using the Zazy Pentest Plugin (zazy-pentest), you agree that:
- You will use it only against systems you own or for which you hold explicit, written authorization to test.
- You are solely and entirely responsible for your own actions and for complying with all applicable local, state, national, and international laws and regulations.
- The author, Anand Jogawade (Zazy), is NOT responsible or liable for any misuse, damage, data loss, or illegal activity carried out with this software. Any such use is the responsibility of the end user alone.
- Unauthorized access to, or testing of, computer systems and networks is a criminal offense and may violate laws including (but not limited to) the U.S. Computer Fraud and Abuse Act (CFAA), the UK Computer Misuse Act, India's Information Technology Act, 2000, the EU's directives on attacks against information systems, and equivalent laws worldwide.
- This software is provided "AS IS", without warranty of any kind, express or implied, as stated in the MIT License. The author assumes no liability for damages arising from its use.
If you do not agree with these terms, do not download, install, or use this software.
Use it ethically. Use it legally. Use it only where you are authorized. 🛡️
Built by Anand Jogawade (Zazy) • github.com/AnandJogawade • Licensed under MIT
penetration testing • bug bounty • red teaming • offensive security • Claude Code plugin • AI security • web/API/mobile/network/cloud pentest
// faq
What is Zazy-Pentest-Plugin-for-Claude?
A Claude Code plugin for authorized pentesting, bug bounty and red teaming - 318 attack skills across web, API, Android, iOS, network, AD, cloud and wireless, with dynamic payloads, CVE auditing and a verifier agent.. It is open-source on GitHub.
Is Zazy-Pentest-Plugin-for-Claude free to use?
Zazy-Pentest-Plugin-for-Claude is open-source under the MIT license, so it is free to use.
What category does Zazy-Pentest-Plugin-for-Claude belong to?
Zazy-Pentest-Plugin-for-Claude is listed under plugins in the Claudeers registry of Claude-compatible tools.
// embed badge

[](https://claudeers.com/zazy-pentest-plugin-for-claude)
// retro hit counter

[](https://claudeers.com/zazy-pentest-plugin-for-claude)
// reviews
// guestbook
// related in Claude Plugins
 🔓
A single CLAUDE.md file to improve Claude Code behavior, derived from Andrej Karpathy's observations on LLM coding pitfalls.
 🔓
Claude Code is an agentic coding tool that lives in your terminal, understands your codebase, and helps you code faster by executing routine tasks, explainin…
 🔓
"CLI-Anything: Making ALL Software Agent-Native" -- CLI-Hub: https://clianything.cc/
🔓financial-services — a Claude ecosystem project on GitHub.